1 free read left. Create a free account for unlimited reading + AI research.
Create free account
Superstar Session: Why Protection Matters?
Key insights
7 takeaways- 01Mobile games now generate 66% of total app store revenue, making the protection of game integrity a critical financial priority for publishers.
- 02Security analysis of the top 50 Google Play Store games shows that 98% are susceptible to tampering, with 49% having active, functional cheat versions available.
- 03Hackers frequently exploit Unity-based games by using automated tools to resolve metadata and identify function offsets, allowing them to crack updates shortly after release.
- 04Memory editing tools like Game Guardian pose a significant threat, with 16% of top-tier mobile titles currently vulnerable to runtime modifications.
- 05Developers can reduce the attack surface by moving critical game logic from the client to the server, effectively eliminating local code that can be patched by unauthorized users.
- 06Fundamental security measures should be integrated during the design phase, including stripping unnecessary engine code, encrypting plain-text strings, and removing descriptive symbol names to hinder reverse engineering.
- 07Advanced protection strategies, such as integrating obfuscation and integrity checks directly into CI/CD pipelines, provide necessary defense against debugging and unauthorized distribution.
Ask AI about this video
Transcript
let's get things started first off this morning we are kicking off with a superstar session uh we're looking at why protection matters with kurt from denuvo by erdetto so let's see if we can pull kurt in from the green room where he's been enjoying a virtual coffee and hopefully a virtual bacon sandwich here he is fabulous joining us through the miracle of technology good morning good morning thanks for having me here not at all thank you very much indeed for agreeing to talk to us this morning um where are you joining us from i'm in austria south carolina fabulous oh what an amazing city i have been there a grand total of once and i had plans to go back and then the world stopped so um i have to get back i have to get back in and autumn and winter are an amazing
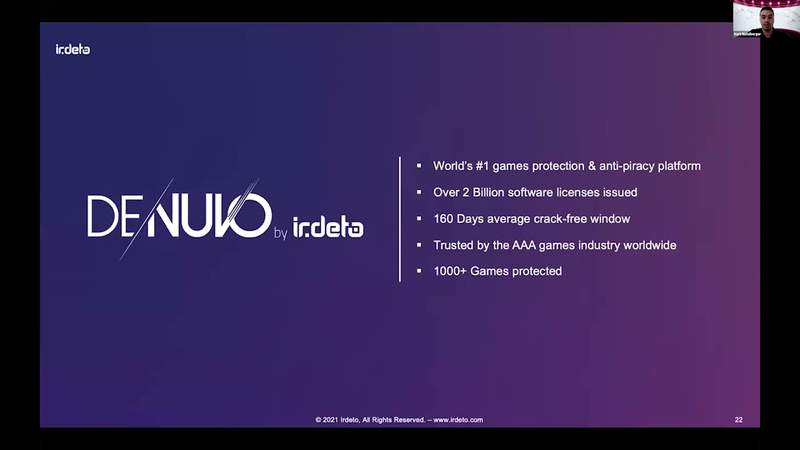
time to go i believe it's also nice in summer but yeah it's most famous for skiing i guess i guess i i i don't ski i fall over um and so the higher the mountain the the further it is to fall but uh i i do love the place are you all ready for us this morning kurt i'm super ready excellent in that case i will fade into the background i will leave you to get on i will join you at the end kurt take it away so i'm i'm curt i'm working at the new bayer data i'm working in the mobile team and as a software engineer and yeah we do mobile production and today i would like to talk about why protection matters in order to protect your revenue from your games i'm sorry okay nitrax so i'm sorry just a second next zoom pops up yeah so the new is world's number one games production platform so it's pretty
well known for all uh protecting most of the pc aaa games right and our parent company at that also brings in a ton of security expertise so and with combined forces we are trying to build a secure future so uh i tried to came up with some numbers about the mobile gaming market and especially last year uh like the demand it highly that they highly grew right which was also because of course but you do it to the pandemic so which is like most amazing to me is like uh the app store like 66 percent from the upstairs revenue actually coming from mobile games so that are some great numbers for us is mobile production also for us game publisher so but also with all this rise also the piracy increased and we had a lot of customers who who noticed like a high increase of cracked games and with this high increase of
tracking the the revenue um decreased of course so this uh so what are the the most uh fred's mobile games fred uh face and the number one is a tempered version so that's like the huge number one especially on android where you uh aesthetically analyze a game you find some weaknesses and then you redress debut your your modified version on ios that the the thing works a bit different because like redistributing an ipa doesn't work that easily due to all apple standards production so what you do there is like you install so-called like tweaks which are cheat scripts and which modify the runtime behavior of your application and so to get a better overview of the the market we this summer we analyzed the top 50 google play store games and checked off so how many cheats are actually available right and we found out that out of this 50
like uh 50 actually had working cheats um 40 i had a cheat available but it wasn't up to date so like the update cycle on mobile is like pretty frequently and once a cheat has to be updated as well and if that isn't done that she doesn't work anymore so in the end it leaves us with uh 49 of tampered versions and taking a a look at the second fret memory editors we also found like 60 16 of all these games had working editor scripts available so summing this up those are pretty scary numbers and um so taking a look at these numbers the the question is of course how how does cheats created in the first place and the two main ways as i already stated are static tampering where you download your the released app you go through the code you find functions
which are worth to patch and modify then you resign it and then you distribute it so that's like on android that's like pretty common on ios the most the most common way are dynamic modifications so you still have this initial step of analysis and then and finding functions but you don't patch it and redistribute it instead you write a script which patches this code at runtime and then you distribute the script instead of a new ipa so having an example of untampered app with the hungry shock game we analyzed i guess was last year so here we can see like the gold is like always the maximum amount and here it's like the cheetah just found a function which returns the gold and then patches it to always return the maximum amount of gold so how this looks in a bit more detail is i'm talking especially about unity games for an hacker it's possible to retrieve or like to get or to resolve all these function
names again and once you find like descriptive function names which are called get currency the attacker doesn't even need to understand the assembly code anymore all he sees is like okay this function returns an integer and is called get currency so most likely it will return the currency and then he simply patches patches it to always return the maximum amount of number what we got in recent years from customers was that they were always surprised on once they have a cracked version out there and they push up that how fast the update gets cracked as well and this is due to cheat automation so on unity games that's especially easy because you take this global metadata file which contains all these function descriptions and then you put it in tools like il to cpp dumper and then you get out like really descriptive names so you take this blob of data put it in trial to cpp dump and what you get out looks like something like that
and next to the function signature you also get and that's important the offset like the offset where this function is in the actual game library so in this step can be easily automated and you know where to apply your patches so taking a look at the second biggest threat is mem which are memory editors so this happens by tools like game guardian and those work you scan through the app memory and just scan for in this case the value 600 just which is the health power of the hero and you find a bunch of locations which contain 600 so you continue your game play you get a bit of damage and out of this value to it previously had stored 600 at least one must be now 480 right because that's most likely than the health failure and in this case we got lucky there is exactly one left if there are still more left you can just do the procedure again
get more damage and hopefully there will be only one left after a while so once we have this one memory location what we can do is we simply freeze it and by freezing it means we continuously write like 600 to it to this memory location every millisecond increasing this memory value we can't get we can die anymore right because it the um the health bar is always reset um so so as this was all like now examples on android same example uh like the same system right there just the distribution works uh different just the distribution is different right like here you distribute this cheat script you install it on your jailbroken device and then yeah you get this nice pop-ups where you
can choose different options of your cheat so talking about all these threats um the next logical question is what we can do against it right so and now i just would like to talk about some simple steps everybody can do in order to to raise the power of security so depending and the first one is enabling optimization so depending on your development ede there are some default settings unfortunately not a lot but there are some so talking about unity you can for example strip the unneeded engine code or minify your java part and on unreal has this really nice settings where you can hide a symbol visibility so symbols are like function names and as we saw before like on descriptive function names you don't want to have that in your final game so and with this option you can disable or like remove them basically if you want to go more into detail
unity has this super nice setting that you can add additional aisle to cpp arcs this means you can directly forward compilation or optimization flags to your compiler and also to your linker and especially the link stuff is pretty nice because on unity what you can do is you can pass in link conversion script so seeing this link conversion script it defines your symbol visibility and the unity game library only needs this idle to see cpp standard functions to be actually exported right so uh setting this link conversion script you can actually reduce um the amount of exported symbols which reduces your final game library by about 15 in comparison to the standard a unity build and we we this is pretty amazing because we get that a lot that customers can't reduce like have troubles reaching
this hundred megabyte apk limit so now it got better with aap but still that existed a lot in the past for unreal you have the same although not that easily accessible but the settings exist in this in the android tool chain five um the second thing is avoiding plain string so we talked about the export but furthermore like just descriptive strings like rules or error messages like error matches i saw a lot in the past and like having some error messages in a function even though you don't have a name you can guess what it this function will be doing just by reading this error messages so a super simple approach to avoid those plain strings is just by not storing this as them as a plain string in your apk instead you encrypt them and only decrypt them once you're using them right so it's the same functionality but save no plain strings anymore
and the third one is moving game critically logic to the server right we saw the example with the get cold gold function but this function doesn't even need to be there right like you could remove it and once you remove the function there is no place to patch like for example you can just simply rewrite it um only to make a server request right you instead of checking the gold on the client what you do is like you send a request to the server and say like oh this player want to buy this item can he afford it and stuff like that so there's no more code in the in the actual client which you can easily patch so just to sum up these simple steps is like enabling optimization about plain strings and move critically logic to the server like increases just the initial amount of time and hacker needs to investigate to crack net
or of course if you don't want to do that you can give us a call and we are of course sure happy to help you with all our experience so how um just talking uh briefly about our product is how this works uh the new mobile production is uh once a customer approaches us we send them out like our integration client which is like a small binary which you can integrate in your ci pipeline and all this this client does is next to the standard apk build it also fetches the llvm bit code uploads both to our servers and then we protect them on our server so we purely work on the llvm bit code which just allows us a great flexibility and a tight integration into the game itself to avoid a performance impact so we protect it and then we send it back so we have a bunch of dynamic production features so integrity verification so those like modified distributions will
not work anymore and of course all these classic checks right like anti-debugging hook detection root detection those emulator detection so while those are all dynamic protections we also have of course static protection so we put obfuscation on top of all these uh kind of protection just if you wanna try and give it a try and analyze it statically in tools like ida you can basically you can't read it anymore with this kind of objection and if you can't read it you can analyze it right so it's actually pretty simple um once you detect uh like one once one of our checks trigger like the game is running on a root device then of course you have to do certain action based on that and instead of simply crashing the app what you can do with our solution is you can send telemetry requests and then
act on your own what you want to do with this player right if you want to ban it or whatever and all these statistics will be provided by our mobile telemetry solution so and the last thing i would like to talk about is so next up my usual product also one of our duties is to monitor protecting protected games so of course once a protected game is out there we also want to know um when it gets cracked and how it gets cracked of course right to improve our solution so and that's this um there was this situation like half a year ago a year ago where we uh where we had where we were monitoring this forum um of a cheat of a game which had like really a lot of cheats and then once the customer approached us yeah please help us and to protect our game and once we applied our production it
was pretty nice to read that um yeah the admin responded um we had a game added production now and my mod will not work anymore so basically what we can say now write this yeah drop down like red and and start celebrating basically but actually that raised the thought in us because like this response from the admin came so quickly and it was so short and then it was like it didn't feel like he really tried right he didn't like thought like that he put a lot of effort in so what we came up with uh based on this experience and of cerrelata's wealth is um the mobile vault so we thought he did as he didn't really try so maybe our super fancy advanced solution wouldn't have been even necessary and a more like a fast and um like a smaller production would have been already enough to keep this kind of hackers away
so with mobile vault we want to address that um address that and want to bring out next to our base product a more fast and lightweight solution with zero performance impact because like most of the protection happens in the game startup and now zero integration so there will be no client anymore so how this works is we could inferiorly directly take um already a release game from the apk play store from the play store i'm sorry protect it on our servers and send back to you so we don't need the lab and bit code anymore but of course now that we can't that tightly integrated but in the end we can still do a lot of security and yeah and then once it's protected we can send it back to you and so like the big thing here is like the zero integration effort it's easy and it's easy to use and yeah we're planning to do the same
on on ios so and that actually concludes my talk we got some great feedback from customers which encourages us and also motivates us and that's it thanks a lot for your attention and i i'm in the discord and i will also yeah i'm open for questions fantastic that's wonderful stuff kurt thank you very much what a uh an intense way to kick off uh the last day of the conference and some really really valuable information in there and uh our audience have been going crazy in the q a there's a lot here and we've got a few minutes left so i'm going to dive straight into the questions if that's okay with you sure sure i try to be faster first question is is it harder to protect children uh on mobile or pc or console sorry again is it harder to protect children on
mobile over pc and console which is the hardest one to sort of take care of of younger players i don't is is mobile a harder platform to provide protection on versus pc and console so yes definitely uh because on mobile you also have like multiple different uh architectures like talking about arm 64 m32 cdx you have just then you have all these different ndk versions and also the same then applies for ios here so you generally just have more to support so you have to be really flexible there that's fantastic thank you and and so one thing that springs to my mind from that is we have new legislation coming in here in the uk the age appropriate design code which is designed specifically to limit um the exposure to children from gaming across all platforms
are you keeping an eye on that kind of legislation and is this something where you think this is going to make a fairly fundamental change because all of a sudden developers and publishers must look after their younger players i i would say that's not really our audience here to really uh focus on children because what we do is like really taking care of the end client and the apk and ensure that the final apk doesn't get like the final game doesn't get modified so if hackers now of course like patch out children protection stuff then we would detect it but uh yeah we don't really target on this kind of stuff yeah no no no that that's understood no it's no problem um oh here's an interesting one does machine learning and ai have an increasing role to play in helping to spot and identify cheating and hacking ah really great question yeah we had that approach in our anti-cheat solution so where we where we are playing around and also
it's also integrated already in uh production but of course that's a a pretty difficult uh a problem but we yeah we are using it yeah that that's that's great to hear that that's really useful here um and here's one uh can developers make sure their code is inherently more secure from the outset are there widely used techniques they should apply at the design and development stage yeah i guess as i mentioned in my talk it's like moving game critically logic to the server there's like a design decision like if you have easy functions which return like just gold or decide if you have like the battle is one or not such a such um code should be in general avoid it or like apply a simple obfuscation right there are also like obfuscation tools which you can apply directly on sieves plus code and then just this code isn't readable anymore and well i think that's it you know you you were really clear and i think that came through in your presentation which is
that that having things out there in in the clear where they can be seen and understood is inherently insecure and uh you know absolutely not best practice so and so this ties into the next question which is as games become more and more based on server side and we move towards cloud gaming is this going to have a major impact will that be inherently more secure well that depends uh depends where the game is running it's only because it's running on the cloud doesn't make it more secure like if the game is then written in web assembly it's still running in your browser and you could cheat in your browser it's just the approach is a different one so and that's also we are trying to come up like because it's moving to the web we're trying to also move our solutions to the web that's that's a great uh a great point um so here's a question from from an anonymous attendee how quickly are we working on
anti-cheating software for competitive mobile games um um working on antigen for competitive mobile games so in the end there there is no such thing like anti-cheat on mobile actually because what you do is you still protect the end client right and the modification helps in the end client if there is no attacks which are directly facing the server api then that's not something we face at the moment yeah okay no that's that's a great point and um from a legal point of view who's whose responsibility is it to protect a game is it the developer you know is it the publisher is it you know who is fundamentally responsible for making sure that the game is is secure well it's the game publishers right every correct game reduces your revenue so in this in the end you want to make sure you want to avoid that to get the maximum out of your game
yeah no that that's understood that's understood and and where do you guys see the the most um attempts that it's the most activity from cheats and hackers is it is it games where you have a a valuable in-game currency or is it particular genres very good question i think what we notice most is that it's like the in-game currency right it's like game like more like these casual games like simple games where you can like just have if you have a lot of in-game currency you can buy all your in-game stuff and that's like the most attacks we see yeah and what's the most what's the most common is it is it just is it cheating to try and and gain an advantage rather than hacking to to steal yeah it's definitely to gain an advantage like yeah the most common one uh are those those distributed modified
android games this like this is huge and this is a huge market and especially in the asian area is gigantic actually so we we had we had a speaker on from google play earlier this week um who went through an awful lot of changes that are happening in the google play marketplace including a move away from you know the plain vanilla apks um so are you are you following this is this something you think might help address that moving a away from apk you mean like moving to aabs right yes yeah but that's not a security feature what you increase is like you get more flexibility and like the app size increases i understand brilliant and improvement in security itself ah okay okay well see that that's that's really useful for me because it's uh i i walked away thinking that security was a part of this and that's really useful to know um and i think the the last question is
focusing on the hidden symbols that that you talked about in your presentation um okay the the uh anonymous attendee has asked can people not copy those hidden symbols as they alter coding for their own gain would copy the hidden symbols for their own game yeah for their own gain for their own advantage sorry for their own game yes well once the symbol is hidden you don't have it but if the symbol is visible you just know you know the magnitude name of the function and then you if you have like a really descriptive function and you know where this function is in the game then you can patch it right so you just want to make sure you avoid all these unneeded exported smooths that's fantastic and well kurt that that's us um out of time i'm afraid because i really really fascinating exploration of an area that i think more more developers and publishers really should be taking very very seriously as they move forward
whatever type of game they're producing thank you very much indeed for joining us this morning it has been absolutely fascinating um look forward to catching up with you on discord and hopefully making sure that everyone who didn't get a chance to ask questions or have their questions answered can find you there thanks a lot i will be available on the discord for at least all of the day wonderful thank you again kurt
Summary
Mobile gaming has experienced significant growth, particularly during the pandemic, with mobile titles now accounting for 66% of total app store revenue. However, this expansion has been accompanied by a rise in piracy and unauthorized game modifications, which directly erode publisher revenue and degrade the experience for legitimate players. The primary threats to mobile game integrity include static tampering—where apps are analyzed, modified, and redistributed—and dynamic modifications, such as the use of cheat scripts or memory editors that alter runtime behavior.
Analysis of the top 50 Google Play Store games reveals that 98% of these titles are susceptible to some form of tampering, with 49% having active, working cheat versions available and 16% vulnerable to memory editing tools like Game Guardian. Hackers often exploit descriptive function names in Unity-based games, using tools to resolve metadata and identify specific offsets for patching. Because these processes are increasingly automated, updates to games are frequently cracked shortly after release.
To mitigate these risks, developers should implement fundamental security practices during the design phase. Key strategies include enabling compiler optimizations to strip unnecessary engine code, removing descriptive symbol names to hinder reverse engineering, and encrypting plain-text strings. Furthermore, moving critical game logic from the client to the server significantly reduces the attack surface, as there is no local code for hackers to patch. While advanced, server-side protection solutions—such as those that integrate into CI/CD pipelines to apply obfuscation and integrity checks—provide robust defense against debugging, hooking, and unauthorized distribution. Ultimately, the responsibility for securing a game rests with the publisher, as protecting the integrity of the client is essential to maintaining revenue and ensuring a fair competitive environment.
Comments