1 free read left. Create a free account for unlimited reading + AI research.
Create free account
GDPR – How to be compliant and what that means for your company
Key insights
7 takeaways- 01Personal data is defined broadly under the regulation to include any identifiers such as IP addresses, device IDs, and social identity markers.
- 02GDPR applies to any entity handling the personal data of EU citizens, meaning companies incorporated outside the European Union are still legally obligated to comply.
- 03Organizations must clearly distinguish between data controllers, who define the purpose of collection, and processors, who handle data on behalf of others.
- 04Non-compliance with GDPR carries severe financial penalties, reaching up to 20 million euros or 4% of a company’s total global annual turnover.
- 05Businesses should audit and update all vendor contracts with necessary addendums to ensure third-party partners align with GDPR disclosure requirements.
- 06To ensure compliance, companies must implement transparent privacy policies, establish robust consent management systems, and maintain detailed records of all data processing activities.
- 07Adopting GDPR compliance measures globally is a recommended strategy to mitigate legal risk and future-proof operations against evolving international privacy standards.
Ask AI about this video
Transcript
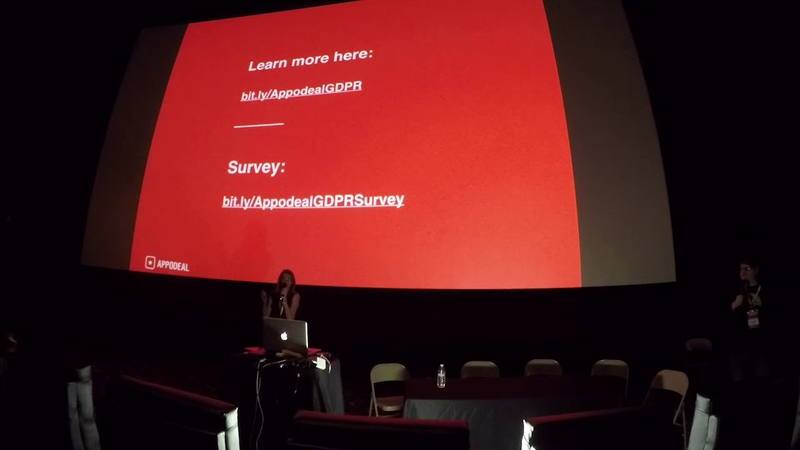
[Music] [Music] thank you so much for coming to to Pocket Gamer connects and thank you so much probably for my speech today I will be talking about this extra ordinarily boring subject of GDP our compliance as you may have found out from the program and thank you for coming thank you for staying if you're leaving then that's a pay before I'm gonna begin I'm gonna ask you guys three questions it's so cool that's like this is I can barely see you so I'm going to ask you three questions can you please raise your hand if you have heard of our GDP
our compliance cool so almost everyone action has heard this is perfect last week I had a webinar and I posted a promo the video promo on a Facebook profile and one of my network connection commented what is that why do I need it why don't you care so that is really nice that I have an audio that is more or less familiar with the subject but I have another question who here is completely confident that they're complying to they're ready for the nature awesome oh where are you from of course you are well so and my third question is a promise who here feels like they need a poker anyway before I'm gonna start to start into the subject I'm going to introduce myself my name is Natalie and
while there's a trick picture me right there Hugh in case you can't see me really well I'm chief operating officer of a body LM also chief evangelist about a deal that means that I have been working with a group of lawyers the subject of GDP our compliance and right now I'm here tell you all about this so to make this subject a little bit less boring and the little bit more entertaining I'm hoping that I will be able to interact with you guys a little bit more so whenever you feel like you have a question in the middle of a slide please raise your fat raise your hand and I'm gonna pass the microphone to you and ask a question if you don't that's okay at the end of the session we're going to have a Q&A session as well where you can ask questions that are all related to certain flats so what is gdpr I'm sure that you all familiar with this but GDP R stands for general data protection population it is a set of laws and laws that are designed to
protect a personal data of all European citizens no matter where they are in the world they Europe they traveling and no matter which role they are doing right now they're at work or they are just a person who is using an app or any person the person is a person about who they are in any of their roles so what is a personal data personal data by GDP are is any kind of data any kind of information that is potentially can link this information to a certain person so this information can include name date of birth indication number Social Security number social identity even their group of friends IP address device IDs pretty much any information that makes it possible to track down a specific person anywhere in the world so who is
responsible before I'm going to jump into separating the roles here the people or the companies who are incorporated in United in European Union our old should be a gdpr compliant that old must be CPR compliant however even if you are incorporated anywhere else in the world the United States Canada France reference but Russia Australia anywhere China but you do work with European companies so you work with European freelancers or employees or even end-users you must be compliant so anyone in this industry must be compliant because we all want more users and they all die located all over the world so most of them are not most of them probably but a good chunk of them are in the European Union so we should all be compliant gdpr to understand
whose fault of a GDP our breach GDP are lost divided roles for controllers and processors who those are you can see the brief description on the screen but controllers are basically at the companies who control the data collection who define why they need this data and what they need is for how long they gonna keep it for what they gonna use it for and so on they are the people or they are the conservative companies that developed the product that will be using this data who are the processors the processors generally speaking are those that stay a little closer and closer to the end user and collect this data if we are talking about the end user the good example of processor would be the publisher so those that actually are the first person who communicates for the end user if we are talking about
attempt like a freelance at App Engine see would be a good processor and the employer who employs a temp worker from this type ng C would be controller and so so any questions on this okay great so on this slide it's going to be clear we explained how in our gaming or attack or gaining ecosystem we define patrollers and processors so that if you just watch this just watch the slide without any sound without me explaining it it looks like the black arrows going to from the advertisers to the end users and resonator and then the error is in Brad go back and put this data so the ultimate controller would be the guy on the left right left who is the advertiser or an agency but
everyone else is Marylyn processor and is not responsible which in reality is actually not true because every each and every of those companies in between the advertiser and the end-user is the company that has their own product so they all require a certain information to work for example I can speak from a video perspective and although their processors for many of our partners we also require information to make our product possible for example product that is provided at a good traffic that is free of fertile activity we need this information to collect this information regardless of word aware this user in the world to make sure that we provide a clean traffic there is no double clicks or no BOTS or so on we need information to provide a good and fair price and provide a high spain add in a real-time
action to publishers so we also need to collect the situation and and so on if any questions on this great so what happens if we are not compliant which is the what I care it's too much legal paperwork it's just it's just so under GDP are we didn't heal with the very very insignificant relations and minor violations will cost the company 10 million euros over two percent of the global turnover which have our greatest or for serious violations if you've not complied at all even a part of GDP our but you keep collecting the data will cost you four percent of the global turnover or 20 million euros whichever is greater so let's all be compliant again GDP our begins on May 25th and there is no grace period in between May 25th and so whatever charity that you
must be complied you must be complied to May 25th GPR has been adopted accepted sorry in 2016 two years ago so these last two years actually that was a grace period ok so I hear I sent multi months with our lawyers working on the GTR compliance for a Badillo and here's the chocolate if you come through you welcome to take a screenshot or take a picture but at the end of this at the end of the session I'm gonna give you a link or guilty you will download the slides as well anyway we developed a new privacy policy we list it clearly what we use the data for which data is being used we listed clearly who our partners are as so the end user potentially can shut down which the unit is being tracked or which data has been collected by a Padilla which data has been collected by any of those 60 demand partners that we use or whoever else
consent management we attack with yield not collect and send ourselves a like mobile we ask our publisher to collect the consent for for us so what that means is we believe that it will not provide the best user experience if every partner of error the publisher would request their own consent if you work with several monetization tools and if you work with several and a little a little tools and you like everyone request their own consent from the ad user before the session begins it will simply run the risk of spoil and user experience so we ask in our publishers and this is listed in our privacy policy that they are collecting the content and the study needs to happen in the abandoned management what it means is that we went through all of our contracts with our
vendors and we made sure that the contracts are GDB of a point well many of those contracts were signed in 2015 2016 and last year and of course there is nothing imaginary to be on there so we instead of rewriting the contracts we are simply sending their addendums to the clients or certain vendors to just simply make sure that we are compliant data processing a mechanism what it means is that a company Apple or any of any other company must keep a list of the products that is using the data that is collecting and using the data so we have a list of all the features that a canoe currently provides apparently provides that is collecting the data even if they were developed in 2016 but
we still keep using them they must be of this team record tracking and the force or the future product that will be collected this data was the capture must be captured this unified document mm-hmm we developed a list of internal procedures that allow everybody clearly to see what happens if a data object or a person requests to delete all the information that the previously collected and look man in the future so all of that is clearly stated in our internal supplementation's for internal use and of course moving forward we'll be demonstrating our ongoing compliance with GDP are in various ways so thank you very much for listening and do you guys have any questions at all please feel free as in right now if you can think of any later then you can just send this message any insults any suggestions please go ahead
and send me a message don't take it away Yin that's right so as promised there was a link the bitly link on top that will we just put all the collateral on gdpr in one place on a midi website and you just follow the link between slash up at you gdpr and you will find the by bernard i mentioned above magic webinar recording you will find several articles you'll find frequently asked questions and answers to those questions and so on also if if you will maybe consider giving me two more minutes of your time and go to the bitter link and completely the survey about today's speech I would be really grateful it's really simple there are only few simple questions so questions
hey one alright so I asked the same question to other lawyers like really how much do should be cared how much should we would be afraid and the thing is the chance that the government agency will come up to you and check if your GD both applied to Thursday but it exists the matter of your epidural and emeriti or twitter or if you are small indie developer it still exists so there so if you are not completely compliant if you're not at all compliant that there is a good chance that they may find you how big of decisions of course I cannot
answer that I've just we don't know but there is a chance so if you are not compliant right now I suggest that you at least take a few very very simple steps like on centrality provide the consent to the end users you develop a very simple privacy policy where lists which information you do collect and keep if any and which lists the list of your partners that you collect this information just to protect yourself just to demonstrate that I'm going to give you our compliance
correct and justify its last year that you started to question the cookie notification pop-up on the human side that this website is using cookies this is also linked to the same duty black appliance and as you know most people just put a little I agree thing and that's a the main move on so this is going to be the same with the concent just simple I don't know like a banner or simple a full-screen banner they just says hey if you play this game you can just just so you know we collect new information and that's it and just a click OK yeah hi this is Kali rice from tango thank you very much for this inside here on GPR I have one question so in theory
of course we're all dealing with now the question is that this will well over to any to how you do with consumers worldwide and not just yeah it's actually a really good question there was a there was a set of laws in the United States released not so long ago called promises shield and it's exactly the same so designed to protect the users and users in terms of which information is being collected but its last strict than GDP are so if your GDP are compliant this is soon sooner or later they hold the rest of the world is gonna catch up so if your GDP are
complying and will make whether that will make you more compliant for any other country out there that is more or less doing this privacy laws privacy shield in the United States so I would recommend just to make sure that you have are that consent for any of the user in the world and regardless of their location just to protect itself and because sooner sooner or later it is it is definitely got you know thank you so much um back you were committed if you are right now and then we are not as you said we're not dealing with you users but it's pretty crazy to think that for example like the user you but people who leave their travel to some other country when they give like a hotel or passport which means the hotel has to be gdpr but I don't think a lot of people are noticing that because you
know that good so how many you are dealing with all the partners how big it was the percentage people actually energy they are complaining or like if people are still getting ready or do you think it's like the most your partner's already well without dealing with the hotels but we are dealing with the advertisement with other partners that are in demand site or the other partners that are no supplies I'd like publishers so we have received a lot of questions from these partners so it seems like people are moving into gdpr compliance more or less and it looks like majority is concerned to make sure that they are compliant if I understand your question correctly if you're asking about people are traveling all over the world and making sure that other people or other companies no matter where they are should be compliant then I would say that is absolutely correct even if you are in a little hotel somewhere in Brazil you
probably will the chances that you get European citizens will be pretty high so just simply place in the privacy policy that say hey by staying in this hotel we're gonna collect your passive information laying dataverse and so on I'm gonna keep it for an ex period of time for these purposes then that would be sufficient but of course with this set of laws being active now every company that has potential of tracking information that potentially can track down the specific user specific person anywhere in the world should be of course compliant so I think that that's all the time you have thank you guys [Applause] [Music]
[Music]
Summary
The General Data Protection Regulation (GDPR) serves as a comprehensive framework designed to protect the personal data of European Union citizens, regardless of their physical location or the nature of their interaction with a service. The regulation defines personal data broadly, encompassing any information—such as IP addresses, device IDs, or social identity markers—that can be used to identify a specific individual. Compliance is mandatory for any entity handling the data of EU citizens, including companies incorporated outside the European Union.
The regulation distinguishes between controllers, who define the purpose and scope of data collection, and processors, who handle the data on behalf of others. In the digital advertising and gaming ecosystem, these roles often overlap, as many intermediaries collect data to ensure traffic quality, prevent fraud, and facilitate real-time bidding. Non-compliance carries significant financial risk, with penalties reaching up to 20 million euros or 4% of global annual turnover for serious violations.
To achieve compliance, organizations must implement transparent privacy policies, establish robust consent management systems, and maintain detailed records of data processing activities. Because the regulation mandates that companies clearly disclose how data is used and who their partners are, businesses are encouraged to audit existing vendor contracts and update them with necessary addendums. While the GDPR is specific to the EU, its principles are increasingly influencing global privacy standards, such as the Privacy Shield in the United States. Consequently, adopting these compliance measures globally is recommended as a proactive strategy to mitigate legal risk and ensure future-proof operations across international markets.
Comments